Job
enquiry:+91-9121642626
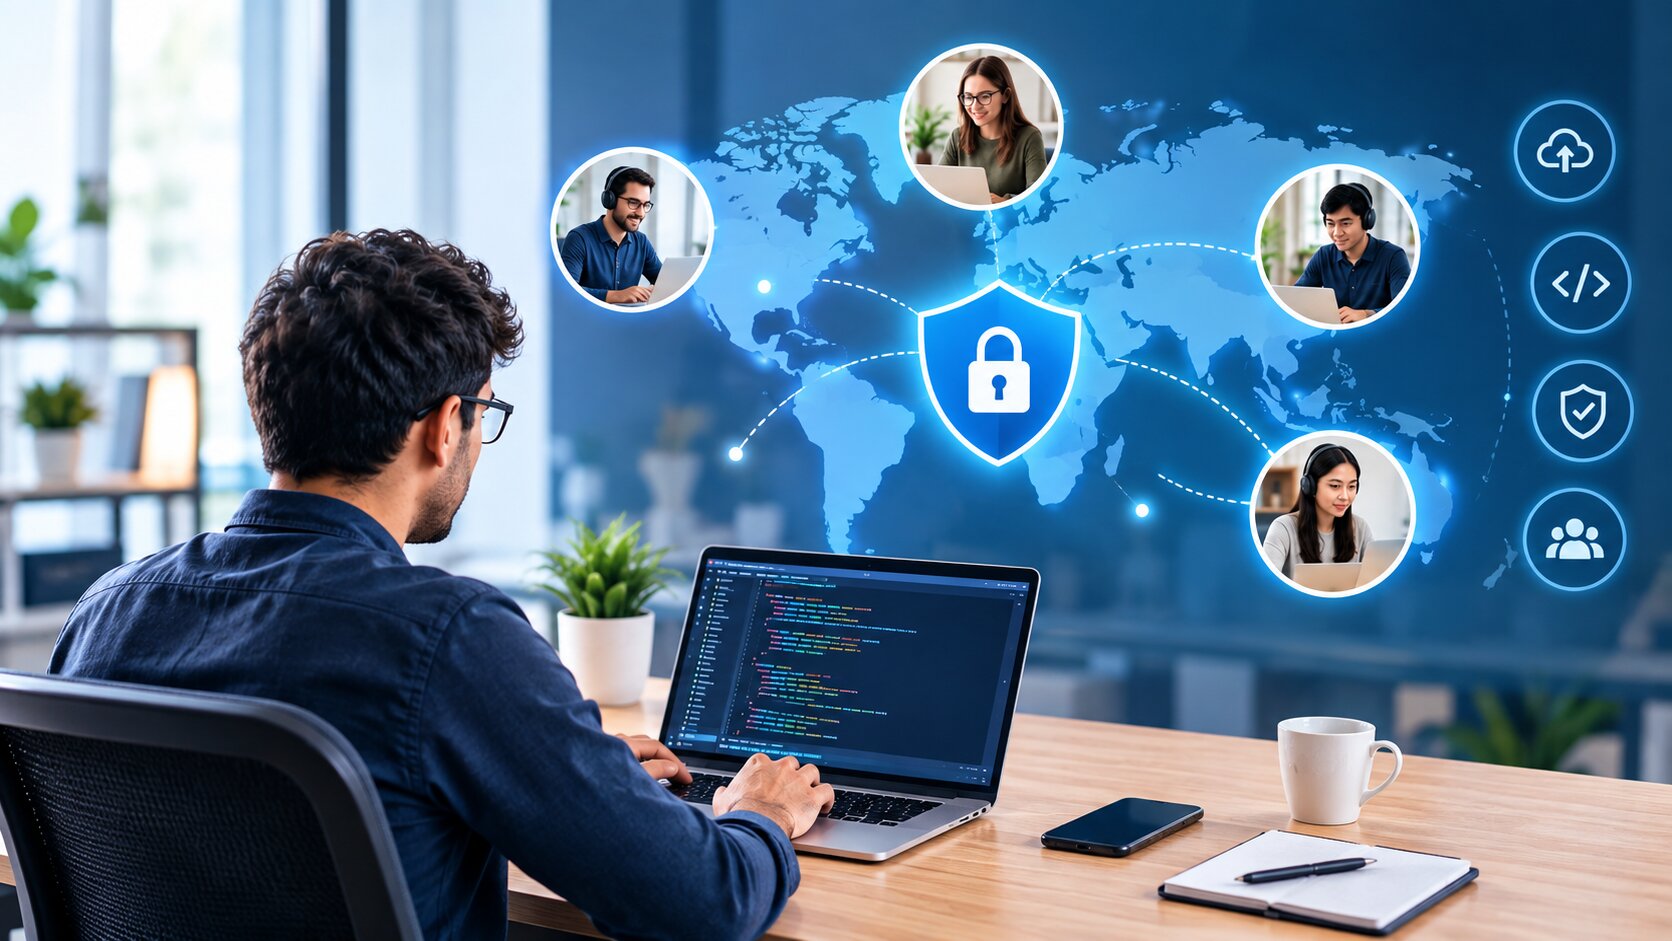
Is It Safe to Outsource Software Development Overseas?
Outsourcing software development has been one of the best and most common ways to save on costs. However, is sending sensitive data to faceless foreign developers actually safe?
The answer: outsourced teams are not inherently riskier to work with than in-house ones. Depending on their data security practices, an outsourced team can be just as secure (or just as risky) as an in-house one.
Of course, since you have less visibility into outsourced teams, real safety comes down to thoroughly vetting for a provider that prioritizes it.
If you’re looking to outsource software development, here’s what you should know—and do—to keep your company’s data, intellectual property, and systems secure.
What "Safety" Actually Means in Outsourcing
When companies ask if outsourcing is safe, they can mean one of three or a combination of three separate things:
- The safety of data and source code.
- The safety of intellectual property.
- The safety of your systems (could the provider's own security gaps become a backdoor into your business?)
Each of these is a different problem with a different fix. Here's how to think about each one, and what to actually check before you sign with a provider.
Data and Source Code Security
Outsourced developers rarely steal data or source code from clients. Leaks are typically the result of simpler, more unintentional mistakes. For example, code not being checked for problems before it gets used, or an employee having access to more data than their job requires.
And a low-ranking employee having access to, for example, admin credentials or a client's full codebase should not be underestimated. As Singapore's Cyber Security Agency has warned, even a single compromised part of the software supply chain can lead to attackers gaining deep access to internal systems.
This means even something seemingly minor, like a single overlooked plugin, script, or third-party tool, can end up causing major operational, financial, and reputational damage.
Responsible developer teams—outsourced or not—will have strict security procedures and will always:
- Keep track of outside tools and code libraries for your project.
- Limit who can touch the live systems your customers actually use.
- Maintain separate environments for testing and production.
Even basic, often-overlooked practices can go a long way, like using strong, unique passwords for every account, or picking the best VPN online for anyone working remotely over public Wi-Fi.
Intellectual Property Protection
Intellectual property questions come down to two things: your contract and your choice of country.
Your contract should be properly drafted and paired with an NDA, explicitly stating that all code, designs, and documentation are your legal intellectual property the moment they're created, and not upon final payment or project completion. This includes work done by subcontractors. It should also outline a clear and detailed process for handing over data if the relationship ends.
Your choice of country matters for a different reason: enforcement. A well-drafted contract is only as strong as your ability to act on it if it gets breached. How enforceable a contract is depends primarily on how quickly local courts move and whether the country is a signatory to IP treaties like Berne or TRIPS. All else being equal, prioritize providers based in countries with a track record of actually enforcing IP and contract claims.
For what it's worth, many major outsourcing countries like India and the Philippines, and some Eastern European countries, have strengthened their IP laws over the past decade.
Either way, no matter what country you’re outsourcing to, consider it a red flag if they hesitate on any of the contract terms above or are vague about subcontractors.
The Safety of Your Systems
If an attacker breaches a provider’s systems first, your system is potentially next in line. After all, if their team has access to your code, servers, or credentials, their security becomes your security—for better or worse.
The practices that matter here should be the bare minimum: do they check their code and outside components for known weaknesses? Do individual developers have only the access they need rather than blanket access to everything? Are passwords and access keys stored encrypted rather than sitting in plain text?
Another thing worth checking to ensure your data is and will be secure: see how a provider is adapting to how attacks have been evolving—or if they know they’ve been evolving at all. According to Verizon's 2026 Data Breach Investigations Report, exploiting software vulnerabilities has overtaken stolen credentials as the leading way breaches begin. The share of employees regularly using AI on work devices has tripled to 45%, and unapproved 'shadow AI' is now a leading cause of non-malicious data leaks.
Go with providers that patch known issues quickly and treat this as routine maintenance.
Vetting a Provider Before You Sign
Of course, most providers will say yes when you ask if they follow these security practices. As such, the real vetting work is in verifying their answers.
A few concrete ways to do that:
- Ask for independent proof, like a SOC 2 or ISO 27001 certification, or a recent penetration test report from a third-party security firm: This is the strongest piece of evidence you can obtain, since it's been checked by someone other than the provider itself. Not every provider, especially smaller ones, will have these certifications, but more and more firms have been getting certified in recent years.
- Ask them to walk you through their security practices, and request it in writing too: A provider with real discipline will answer specifically and without hesitation, and can back it up with a written policy naming actual practices: how they patch known issues, how they manage access, how they store credentials.
While this is still self-reported, it’s at least useful for spotting a provider who clearly hasn't given security much thought. - Ask for references from long-term clients, not just a portfolio, and actually call them: Ask the reference whether the provider's stated security practices held up over time or if they’ve encountered any leaks or issues while working with the provider.
- Run a small paid trial project before committing to anything long-term: Use it to watch how they manage access, document decisions, and communicate under low stakes. Such behavior tends to hold steady once the stakes go up.
- Ask exactly how they revoke access when someone leaves the project, and how quickly it happens: If they say they revoke access on the same day, it’s a good sign.
- Ask how they'd handle the first 24 hours after a breach: Specifically, ask them who gets notified, how fast, and what they'd tell you. A provider that's thought this through will have a clear answer; a provider that hasn't will improvise one on the spot.
- Have a lawyer review the contract: This ensures your contract is legally sound, realistically enforceable, and includes every relevant protection possible, including clear terms for data handling (GDPR or HIPAA, where relevant), breach notification timelines, audit rights, and where your data is stored and how it's deleted afterward.
Aside from the lawyer, consider also hiring a technical consultant to independently assess a provider's security practices if you don't have in-house technical staff who can do that for you.
The Bottom Line
Outsourced or in-house, what keeps your data, IP, and systems safe is having a team with real security discipline, a thorough contract and NDA, and whether you've verified both before relying on them for something important.
And remember: a contract only helps after something's gone wrong. Too many companies think it’s the only safeguard they need. It lets you sue or walk away, but it rarely undoes the damage.
Vetting the provider properly—by asking questions, verifying their answers, and getting the right terms in writing—before you sign, is what actually prevents it.
FAQ
Q: Is it riskier to outsource software development to an overseas team than to hire locally?
A: Not inherently. The risk primarily depends on the development team’s cybersecurity practices (or lack thereof). An in-house team with lax security practices puts your data and IP at more risk than an overseas company with strict ones.
However, overseas teams do carry unique risks due to the distance. Enforcing a contract, verifying practices, and coordinating quickly if something goes wrong are not as straightforward as they would be with a local team.
Regardless of where they're from, evaluate providers individually on their security practices, references, and willingness to put data protection and IP terms in writing.
Q: How can I protect my intellectual property when outsourcing overseas?
A: Start with a thorough, legally sound contract. It’s your best defense against intellectual property theft. Your contract should state that all code, designs, and documentation belong to you the moment they're created, including work done by any subcontractors. It should also include a thorough handover process in case the arrangement ends.
Also, choose a country that makes it easy to enforce said contract. Look at how quickly local courts move and whether the country is a signatory to IP treaties like Berne or TRIPS.
Q: What security questions should I ask a potential outsourcing partner?
A: Ask whether they patch known vulnerabilities quickly, whether individual developers only have access to what they need, and whether credentials are stored encrypted rather than in plain text.
However, don't take a confident "yes" at face value. Ask for evidence, like a SOC 2 or ISO 27001 certification, or a recent penetration test report from an independent firm. A provider with real discipline will have this on hand; one that only offers a written policy or a verbal assurance hasn't been independently checked, which means you're still taking their word for it.
Q: Do outsourcing destinations like India or the Philippines have adequate data protection laws?
A: Yes. Many major outsourcing hubs, including India, the Philippines, and parts of Eastern Europe, have strengthened their IP and data protection laws to make themselves more attractive to foreign clients, since so much of their software export economy depends on being trusted internationally.
That's a reasonable starting point, but laws on the books don't guarantee enforcement in practice. Check the country's track record for actually upholding IP and contract claims in court, not just whether the relevant laws technically exist. And regardless of country, vet the individual provider's practices directly rather than assuming any legal framework alone protects you.
Q: What contract clauses matter most for keeping an outsourced project secure?
A: Prioritize a clause stating you own all work products, including anything created by subcontractors, along with a strict confidentiality agreement.
Add data handling terms aligned with regulations relevant to your business, such as GDPR or HIPAA, where applicable, plus a clear timeline for being told if something goes wrong.
Include the right to periodically check the vendor's security practices, and state clearly where your data is stored, and how it's deleted once the engagement ends, so nothing is left ambiguous after the relationship wraps up.
 Whatsapp
 Email