Job
enquiry:+91-9121642626
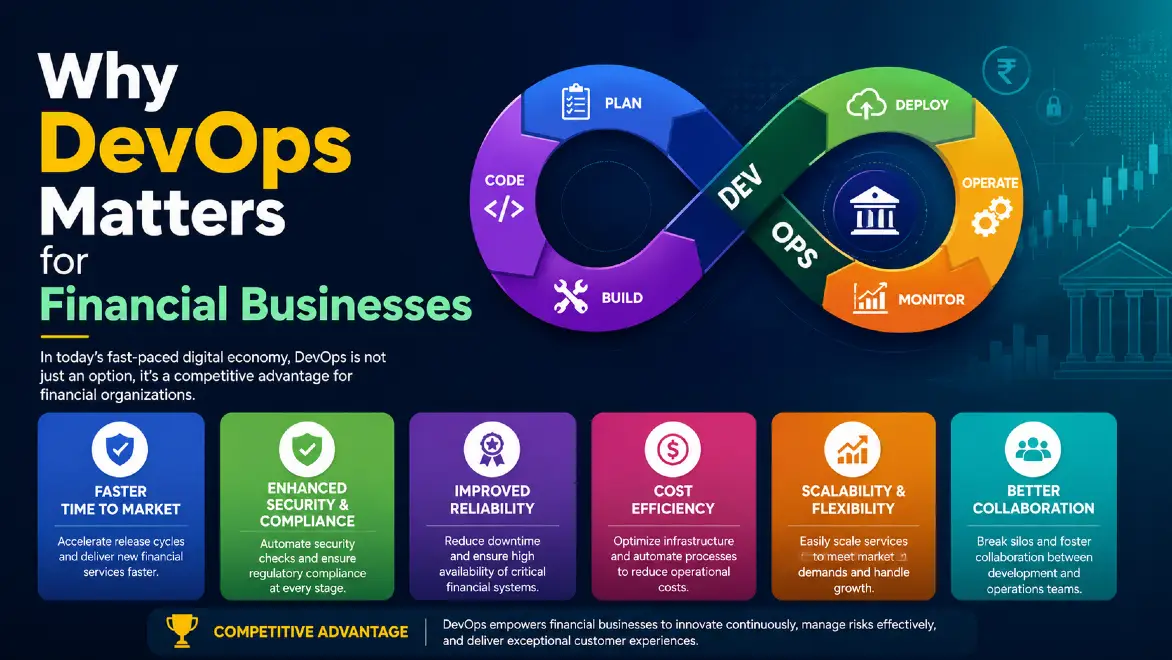
Why DevOps Matters for Financial Businesses
DevOps is, by nature, a centralized way of working: rather than distributing tasks across separate departments with a formal handoff between them, one team owns an application's development end to end. That's a real cultural shift for financial businesses specifically.
Distinct teams with narrow specializations, and a deep, often well-earned caution around changing anything that currently works, has historically been the norm rather than the exception in this industry.
That caution made sense for a long time. It doesn't anymore, or at least not in the blanket way it used to.
DevOps adoption in financial services has moved well past the experimental stage. This isn't "only a handful of banks" testing the waters, it's standard practice at major institutions, and the regulatory landscape itself has evolved specifically to expect the kind of rigorous, automated, well-documented technology practices DevOps enables. Here's what actually matters for a financial business evaluating this in 2026.
Speed, backed by real current data rather than a decade-old stat
DevOps' core structural advantage is straightforward: with one team responsible for an application from start to finish, development never fully stops for a handoff the way it does under a traditional waterfall process, where work sits idle while it moves between business, development, and IT departments in sequence.
The often-repeated claim that DevOps enables 30 times faster deployment traces back to research that's now roughly a decade old and has been meaningfully refined since. Current industry benchmarking (from DORA, the DevOps Research and Assessment program, not to be confused with the EU financial regulation of the same name covered below) has moved away from a simple multiplier entirely.
As of 2025, the research replaced its older four-tier performance model with seven distinct team archetypes based on actual, observed metric combinations. The current data shows a real, wide gap: only around 16 percent of organizations achieve genuine on-demand deployment, multiple times a day, while close to a quarter still deploy less than once a month.
The gap between top and bottom performers remains dramatic. Trunk-based development, where every change merges to a single branch through an automated pipeline, shows up in 89 percent of top-performing teams against just 23 percent of the lowest-performing group.
For a financial business evaluating DevOps, the honest takeaway isn't a flat multiplier. It's that the gap between doing this well and doing it poorly is large, measurable, and worth taking seriously, rather than assuming any DevOps adoption automatically delivers dramatic speed gains.
Improved processes and genuine cross-functional teamwork
DevOps works by bringing people, technology, and process together deliberately rather than leaving them siloed. When developers, operations, and business stakeholders share real accountability for an application's outcomes rather than handing responsibility back and forth, it naturally encourages better practices and a more streamlined way of actually solving problems, rather than each department optimizing for its own narrow slice of the process.
For larger financial institutions specifically, this increasingly takes the shape of Platform Engineering, a dedicated internal team building standardized, self-service deployment and infrastructure tooling that individual product teams use without each one needing to become infrastructure and security experts independently.
This matters more in a regulated environment than it does elsewhere, since it lets an institution enforce consistent security and compliance guardrails centrally, rather than hoping every individual team implements them correctly and consistently on their own.
Cost-effectiveness, genuinely rather than just faster deployment
Faster deployment cycles do reduce development time and cost, that part of the original case for DevOps holds up. But the more durable cost advantage for financial businesses specifically comes from cloud infrastructure adoption alongside DevOps practice: avoiding the capital expense and long lead times of physical hardware procurement, and gaining the ability to scale computing resources up or down based on actual demand rather than provisioning for worst-case peak load year-round.
For an industry with genuinely variable transaction volume, trading system load around market open and close, payment processing spikes around common billing dates, that elasticity is a real, ongoing cost advantage, not just a one-time efficiency gain from faster releases.
Faster, more useful feedback loops
With one team owning an application end to end, both the operations side internally and customers externally have a direct, fast path to report issues. Developers can address bugs and discrepancies without waiting for a problem to work its way through several departmental handoffs first.
In a regulated environment, this matters beyond user experience: faster internal feedback loops mean issues get caught and documented earlier, which directly supports the kind of timely, well-evidenced incident response regulators increasingly expect, covered in detail below.
Security and regulatory compliance: the section that actually matters most for this industry
This is where the original version of this article was thinnest, a vague line about a "myth" being "debunked," and it deserves real depth given how much has changed specifically for financial businesses in the last two years.
A real, binding EU regulation, also called DORA, has made rigorous ICT practices a legal requirement, not just good practice. The Digital Operational Resilience Act, EU Regulation 2022/2554, has been in force since January 17, 2025. It applies to over 22,000 financial entities across the EU, banks, insurers, investment firms, payment institutions, and crypto-asset service providers among them, along with the critical technology vendors that serve them.
It rests on five pillars: ICT risk management, incident reporting, resilience testing, third-party oversight, and information sharing. Non-compliance carries real financial teeth, fines of up to 2 percent of global annual turnover or €10 million, whichever is higher.
2026 specifically marks a shift in enforcement posture. Regulators have moved from reviewing paperwork to demanding real-time, demonstrable proof of resilience, described by supervisors as "interventionist supervision" rather than a passive compliance check. In the 2024 dry-run exercise ahead of full enforcement, only about 6.5 percent of firms passed all 116 data quality checks in the required Register of Information, a clear signal that treating this as a checkbox exercise rather than a genuine operational capability is not going to hold up under real scrutiny.
This is precisely where mature DevOps practice earns its keep. Infrastructure as code and consistent, automated deployment pipelines produce exactly the kind of audit trail and reproducible environment configuration regulators are now asking institutions to demonstrate on demand rather than document retroactively.
Automated testing and staged, monitored rollouts directly support DORA's resilience testing pillar, including the requirement for significant entities to undergo Threat-Led Penetration Testing at least every three years under the TIBER-EU framework. And centralized incident tracking, a natural byproduct of the faster feedback loops covered above, supports DORA's strict incident reporting timelines far better than a fragmented, multi-department process ever could.
The regulation also directly addresses AI, an area moving quickly enough that it's worth flagging specifically. Germany's financial regulator, BaFin, issued guidance in January 2026 clarifying that AI systems, including generative AI and large language models used within a financial institution's technology stack, aren't subject to a separate compliance regime but need to be fully embedded into existing ICT governance and risk frameworks under DORA.
For any financial business incorporating AI-assisted development or AI-powered products, and most now are, this means the same DevOps-enabled governance and audit trail discipline needs to extend explicitly to how AI systems are built, tested, and monitored, not treated as a separate, less-scrutinized category of technology.
None of this is unique to EU-based institutions. DORA's third-party oversight provisions extend to critical ICT vendors serving EU financial entities regardless of where those vendors are headquartered, and the regulation is increasingly cited as a de facto global benchmark, with institutions in North America and Asia-Pacific aligning their own practices to it to remain interoperable with EU counterparts and clients.
If your financial business isn't in scope today, the trajectory of the industry suggests these expectations are becoming the norm well beyond the EU specifically.
Real institutions have already made this shift
This isn't a hypothetical case being made to a skeptical industry anymore. Major banks have publicly documented significant DevOps and cloud-native transformations over the past several years, Capital One's well-known move to an all-in cloud infrastructure being one of the most frequently cited examples in the industry, alongside substantial, sustained technology modernization investment from institutions like JPMorgan Chase.
The direction of travel across the sector is consistent: DevOps and cloud-native infrastructure have moved from a differentiator a handful of forward-leaning institutions experimented with, to close to a baseline expectation for any financial business serious about both operational efficiency and regulatory readiness.
What this actually requires operationally
A few practices worth building deliberately, given the regulatory stakes specific to this industry. Segregation of duties within deployment pipelines, so no single individual can both write and independently deploy a change to production without a second, documented approval, a control regulators specifically look for.
Immutable infrastructure, where servers and environments are replaced rather than modified in place, which produces exactly the kind of clean, reproducible audit evidence DORA's Register of Information requirements are pushing institutions toward. And genuine, tested incident response procedures, not just a policy document, but a process that's actually been exercised, since DORA's resilience testing pillar increasingly expects demonstrated capability rather than a written plan sitting untested in a drawer.
Navigating the broader technical landscape this depends on, from challenges of cloud computing that come with any regulated cloud migration, to the specific data residency considerations that come up constantly in financial services, worth understanding through the lens of sovereign cloud requirements if your institution operates across multiple jurisdictions, is a genuinely specialized undertaking, not a generic DevOps rollout.
Deployment practices that specifically serve a regulated environment
Beyond the general DevOps toolkit, a few specific practices are worth calling out because they map directly onto what regulators are actually asking financial institutions to demonstrate.
Blue-green and canary deployments let a new version of an application roll out to a small percentage of real traffic first, with full monitoring in place, before a complete cutover. For a financial business, this isn't just a best practice for catching bugs early, it's a genuine risk-management control.
If a new release introduces an unexpected problem, the blast radius is contained to a small slice of transactions rather than the entire customer base, and rollback is fast and clean rather than a scramble. This maps directly onto the kind of operational resilience regulators are increasingly asking institutions to demonstrate, not just claim on paper.
Feature flags, which let a team toggle new functionality on or off without a full deployment, give financial institutions a genuinely useful lever during an incident. A problematic feature can be disabled instantly for all users while a fix is developed, rather than requiring an emergency rollback of an entire release.
This kind of fast, granular incident response capability is precisely the sort of demonstrable resilience the shift toward "interventionist supervision" described above is pushing institutions to actually prove, rather than simply assert in a policy document.
Comprehensive, centralized logging and observability, covering not just application errors but infrastructure changes, deployment events, and access patterns, turns what used to be a reactive, multi-system forensic exercise after an incident into something closer to real-time visibility.
Given DORA's strict incident reporting timelines and the broader industry shift toward supervisors expecting real-time evidence rather than retrospective documentation, this observability investment has moved from a nice-to-have operational convenience to something close to a compliance necessity in its own right.
Software supply chain security, a growing piece of the compliance picture
This deserves specific attention because it's a rapidly growing area of regulatory focus that the original advice on this topic had no way of anticipating. DORA's third-party oversight pillar doesn't stop at the vendors a financial institution directly contracts with, it extends conceptually to the full chain of software dependencies, libraries, open-source components, and third-party APIs, that make up any modern application.
A vulnerability introduced through a compromised or poorly maintained upstream dependency is, from a risk management perspective, functionally similar to a vulnerability in code written in-house, and regulators are increasingly expecting institutions to be able to answer detailed questions about exactly what's running in their production environment.
DevOps practices genuinely help here, but only when supply chain security is treated as a deliberate part of the pipeline rather than an afterthought. A software bill of materials, an automatically generated, current inventory of every dependency and its version running in production, generated as part of the standard build pipeline rather than compiled manually when a regulator asks, is quickly becoming a practical necessity rather than a nice-to-have.
Automated dependency scanning integrated directly into CI/CD, flagging known vulnerabilities in third-party libraries before they ever reach production, closes a gap that manual security reviews conducted periodically simply can't keep pace with, given how frequently new vulnerabilities are disclosed across the open-source ecosystem a typical financial application depends on.
The talent and organizational side of this shift
None of the technical practices above work well without the organizational change to support them, and this is worth being honest about rather than treating DevOps adoption as purely a tooling decision. Financial institutions historically built deep, siloed expertise, a security team, a compliance team, a development team, an operations team, each with real domain knowledge but limited day-to-day interaction with the others.
DevOps, done properly, doesn't eliminate that specialized expertise, it changes how it's applied, embedding security and compliance thinking directly into the development process through automated gates and shared tooling, rather than treating them as a separate review that happens at the end.
This has real hiring and training implications worth planning for explicitly. Developers on a DevOps-mature financial services team increasingly need working familiarity with the compliance implications of their technical decisions, not just the technical decisions themselves, and compliance and risk teams increasingly benefit from enough technical fluency to engage meaningfully with automated tooling and pipeline design, rather than reviewing finished work after the fact.
Institutions that invest in this cross-training tend to see the DevOps transformation actually stick, while those that layer new tooling on top of an unchanged organizational structure tend to see the old friction simply reappear in a new form.
The bottom line
DevOps genuinely benefits financial businesses: faster development cycles backed by real current data rather than an old multiplier, better cross-functional collaboration increasingly organized through platform engineering, real cost advantages from cloud elasticity, and faster feedback loops. Most consequentially for this specific industry, it delivers technology practices that directly support meeting a binding regulatory framework with real financial penalties attached.
The old hesitation, "if it isn't broken, why fix it," has been overtaken by a regulatory environment that increasingly expects the kind of rigor, automation, and demonstrable resilience DevOps done well actually produces.
Implementing this well in a regulated environment takes real, specific expertise, not a generic DevOps rollout borrowed from a less-regulated industry. Working with an experienced DevOps development partner who understands both the technical practice and the regulatory stakes specific to financial services is what separates a compliant, resilient transformation from an expensive project that still leaves real gaps a supervisor will eventually find.
Frequently Asked Questions
Is DevOps actually widely adopted in financial services now, or still uncommon? It's now standard practice at major institutions rather than a niche experiment. Capital One's public shift to all-in cloud infrastructure and sustained technology modernization investment from institutions like JPMorgan Chase are among the most frequently cited industry examples, and the trajectory across the sector has moved DevOps and cloud-native infrastructure from a differentiator to close to a baseline expectation.
What is the EU's DORA regulation, and how is it related to DevOps? DORA, the Digital Operational Resilience Act (EU Regulation 2022/2554), is a binding EU law in force since January 2025 requiring financial entities to demonstrate rigorous ICT risk management, incident reporting, and resilience testing, with fines up to 2 percent of global annual turnover for non-compliance. It's a different DORA from the DevOps Research and Assessment program that studies software delivery performance, though the connection is real: mature DevOps practices like infrastructure as code, automated testing, and centralized incident tracking directly produce the kind of audit trail and demonstrable resilience the regulation requires.
Does DORA only apply to financial institutions physically based in the EU? No. DORA's third-party oversight requirements extend to critical ICT vendors serving EU financial entities regardless of where those vendors are headquartered, and the regulation is increasingly treated as a de facto global benchmark, with institutions in North America and Asia-Pacific aligning their practices to remain interoperable with EU counterparts.
How does DevOps help with financial services security specifically, beyond general good practice? Automated, consistent deployment pipelines and infrastructure as code produce reproducible, well-documented environments that are far easier to audit than manually configured systems. Automated testing and staged rollouts support regulatory resilience testing requirements, and centralized incident tracking, a natural result of unified DevOps team ownership, supports the strict incident reporting timelines regulations like DORA now require.
Is the old claim that DevOps enables 30 times faster deployment still accurate? That figure traces back to research that's roughly a decade old and has since been substantially refined. Current DevOps performance research no longer uses a single multiplier, and instead identifies distinct performance archetypes based on real, observed practices. The consistent, current finding is that the gap between high- and low-performing teams remains large and measurable, for example, trunk-based development shows up in 89 percent of top-performing teams versus 23 percent of the lowest-performing group, rather than a fixed speed multiplier applying automatically to any DevOps adoption.
Should a financial business incorporating AI features worry about additional compliance requirements? Yes, and this is a fast-moving area worth tracking closely. Regulatory guidance, including from Germany's BaFin in January 2026, has clarified that AI systems used within a financial institution's technology stack, including generative AI, aren't a separate compliance category, they need to be fully embedded into the same ICT governance and risk frameworks required under regulations like DORA, which means the same audit trail and testing discipline DevOps practices provide needs to extend explicitly to AI-related development.
What are blue-green and canary deployments, and why do they matter for financial institutions specifically? They're deployment strategies that roll a new release out to a small percentage of traffic first, with full monitoring, before a complete cutover. Beyond catching bugs early, they function as a genuine risk-management control for a financial business, containing the impact of an unexpected problem to a small slice of transactions and enabling fast, clean rollback, which maps directly onto the kind of operational resilience regulators increasingly expect institutions to demonstrate rather than just claim in policy.
How does software supply chain security relate to financial services compliance? Regulatory frameworks like DORA extend third-party oversight expectations conceptually to the full chain of software dependencies an application relies on, not just directly contracted vendors, since a vulnerability in an open-source library carries similar risk to one in code written in-house. Practices like automatically generated software bills of materials and automated dependency scanning integrated into CI/CD are becoming close to a practical necessity for demonstrating this level of visibility to regulators.

 Whatsapp
 Email